Is single sign-on secure? See how SSO works, where it fails, and the MFA, key protection and monitoring controls Singapore security teams should require.
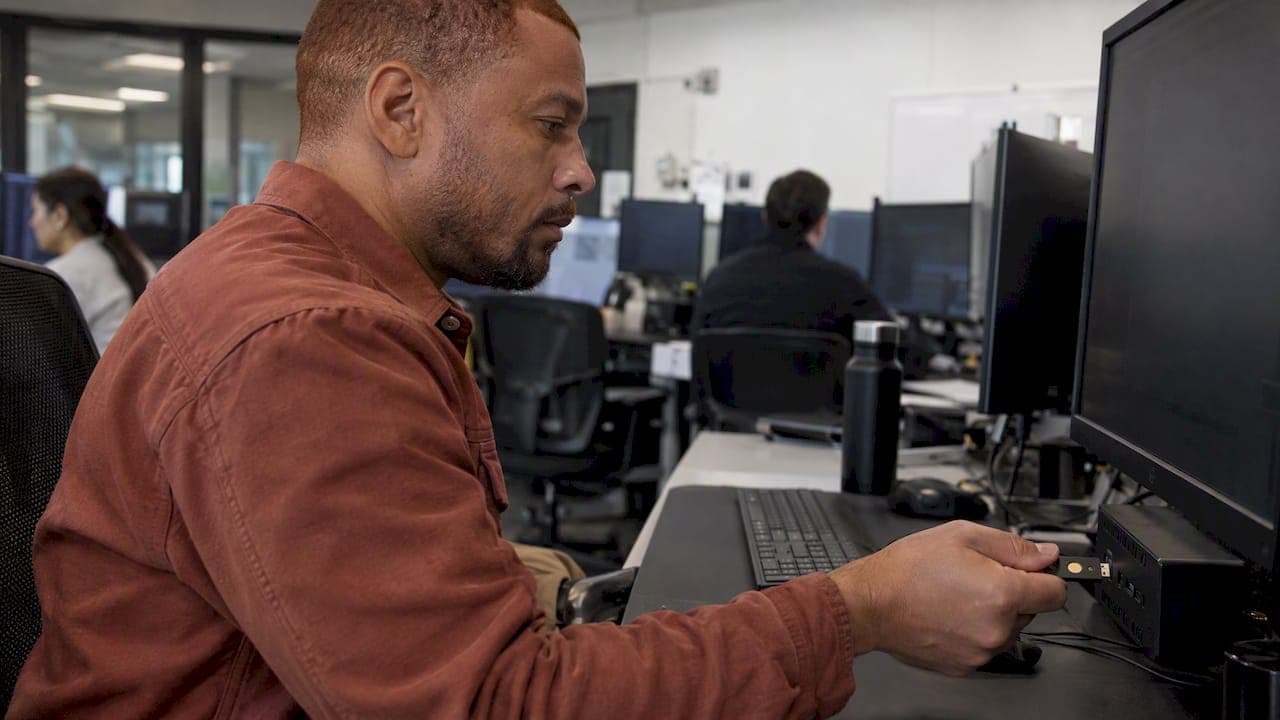
Single Sign-On Security: Risks, Controls and a Checklist

Single sign-on (SSO) is secure when the identity provider behind it is hardened, and risky when it is not. SSO replaces many passwords with one trusted login, which removes weak and reused credentials, but it also turns the identity provider into the highest-value target in your estate. For security managers in Singapore, the answer is not to avoid SSO. It is to protect the login with phishing-resistant multi-factor authentication, guard the signing keys, limit what each user can reach and watch every authentication event.
TL;DR
- SSO lets a user sign in once with an identity provider and reach many applications. That cuts password sprawl but concentrates risk in one place.
- If credentials or assertion signing keys are stolen, an attacker can reach many connected applications at once, so MFA and key protection are not optional.
- Singapore's Cyber Security Agency (CSA) and the PDPC both point to MFA, role-based access, least privilege and logging as the core controls.
- Before you connect any application, inventory it, assess its risk and confirm it validates tokens properly.
- SSO secures the digital door. Facilities and industrial sites still need the same discipline on the physical side, where the same identity logic applies to guards, visitors and contractors.
Table of Contents
- What single sign-on does
- Is single sign-on secure?
- How attackers go after SSO
- Controls that make SSO safe
- Before you connect an application
- Singapore requirements and guidance
- Perspective: identity is a physical security problem too
- Bringing it together in the security operations room
- Where BeyondSensor fits
- A practical rollout sequence
- FAQ
- Sources
What single sign-on does
SSO is an authentication method in which a user signs in once with a centralized identity provider (IdP) and then reaches several applications without entering credentials again. Behind the scenes, the IdP and each application, called a service provider, build a cryptographic trust relationship. The IdP validates the user and issues a token or assertion. The service provider checks that assertion and grants access (Auth0).
Two open standards carry most of this traffic: SAML and OpenID Connect (OIDC). They define how identity claims are communicated, validated and protected against attacks such as token replay (IDManagement Enterprise SSO Playbook). Singapore's own government developer platform uses OAuth 2.0, OIDC and SAML 2.0 for identity and access across its developer services (GovTech Singapore), so these are not exotic choices.
There is also a consumer-style variant. Federated SSO via OIDC lets people log in with an existing account from a trusted provider, so they do not need a new password and they inherit that provider's security measures (CSA advisory AD-2025-015).

Is single sign-on secure?
Yes, if it is properly implemented, and the qualifier carries the weight. The U.S. federal identity guidance describes SSO as secure when done well, while naming the central problem: it can act as a single point of failure and a high-value target. If user credentials or assertion signing keys are compromised, attackers can gain broad and persistent access across many integrated applications (IDManagement).
The international view is similar. ITU-T Recommendation X.1283 says SSO and federated authentication can strengthen security by reducing the risk of managing many passwords, provided the underlying authentication process is strong and properly secured (ITU-T X.1283). It also warns that in federated systems the authentication assurance level matters a great deal, because it sets the aggregate protection for every service behind the login.
Put simply, SSO does not make a weak login strong. It makes whatever login you have more valuable.
What SSO improves
- Fewer passwords. Users keep one primary set of credentials, so there are fewer reused, written-down or guessable passwords.
- One place to enforce policy. MFA, session length and access rules can be applied centrally instead of app by app.
- Faster offboarding. Disabling one identity can cut access to every connected application.
- Better visibility. Authentication events land in one log stream you can monitor.
What SSO concentrates
- One credential, many doors. The chief risk is that stolen credentials could give an attacker most or all applications, which is why IBM stresses strong passwords and MFA as part of any implementation (IBM).
- Signing keys. Whoever holds the keys that sign assertions can forge identities.
- A single outage or compromise. If the IdP is down or taken over, everything behind it is affected.
How attackers go after SSO
The attacks are not theoretical. CISA notes that exploiting SSO is a prevalent attack vector, citing "Golden SAML" cases where adversaries bypassed federation services to gain broad enterprise access (CISA identity and access management guidance).
Closer to home, CSA's 2025 alert on the SCATTERED SPIDER campaign reports that in almost all observed 2025 incidents the group used vishing, meaning voice phishing, to compromise Entra ID, SSO and VDI accounts. From there it reached integrated SaaS platforms to find data that supported lateral movement or extortion (CSA alert AL-2025-066).
The lesson for a facility or security operations team is that the human help desk is part of the attack surface. A caller who convinces a service desk to reset a credential does not need to defeat any cryptography.
Controls that make SSO safe
The guidance from CSA, the U.S. federal playbook and ITU-T converges on a short list. Here it is, in the order we would tackle it.
1. Phishing-resistant MFA on the identity provider
MFA, especially phishing-resistant methods, is critical to preventing unauthorized access (IDManagement). CSA's advice to organizations is to mandate MFA, apply robust role-based access control and least privilege, and monitor for anomalous application usage (CSA alert AL-2025-066).
CSA also frames the choice honestly. SSO through OIDC offers high ease of use, but it is less suitable when you need strong, independent control over account security (CSA advisory AD-2025-015). For administrator accounts, security consoles and anything that touches safety systems, treat that sentence as a rule: use stronger, separately controlled authentication.
2. Protect assertion signing keys
The federal playbook recommends hardware-based storage for signing keys. It notes that NIST SP 800-63C-4 requires at least FIPS 140 level 1 storage for FAL2 and FAL3 assertion signing keys, and that FIPS 140 level 2 or higher HSMs or TPMs are highly recommended (IDManagement). If your IdP is a managed service, ask the provider how keys are stored and rotated. If you run it yourself, this is the control that separates a contained incident from a Golden SAML event.
3. Role-based access and least privilege
SSO answers "who are you?" It does not answer "what may you do?" Singapore's PDPC states that authorization should follow authentication, with access rights defined by role and reviewed regularly so people hold only the access their function needs (PDPC Guide to Securing Personal Data in Electronic Medium). A single login that opens every application with full rights is the worst version of SSO.
4. Monitor successful and failed events
Continuous logging of both successful and failed access events lets teams spot and respond to suspicious activity quickly (IDManagement). Practical signals include logins from new locations, impossible travel, repeated MFA prompts, new device registrations and administrators changing federation settings. Feed these into the same monitoring workflow you use for physical alarms, so one team sees both.
5. Validate tokens and assess identity risk regularly
Applications should validate tokens against trusted sources, and agencies are advised to carry out regular Digital Identity Risk Assessments (IDManagement). Run the same exercise at least once a year, and after any major change to your IdP or federation trust.
Before you connect an application
The playbook is clear that organizations should perform thorough application inventories and risk assessments before integrating new apps into an SSO environment. They should prioritize strong authentication, apply least privilege, and make sure integrations follow security policies and monitoring requirements (IDManagement). In practice, a pre-connection checklist looks like this:
| Check | Question to answer | Red flag |
|---|---|---|
| Inventory | Who owns the app and who uses it? | No named owner |
| Data sensitivity | Does it hold personal data, video or access records? | Sensitive data with no extra controls |
| Protocol | Does it support SAML or OIDC with signed assertions? | Shared passwords or proprietary tokens |
| MFA | Is MFA enforced at the IdP for this app? | MFA exempted "for convenience" |
| Roles | Can it map IdP groups to least-privilege roles? | Single all-access role |
| Logging | Does it send auth and admin events to your monitoring? | No exportable logs |
| Offboarding | Does disabling the identity end sessions quickly? | Long-lived local sessions |
If an application fails two or more of these, keep it outside SSO until the vendor fixes the gap, or place it behind additional controls.
Singapore requirements and guidance
Under the PDPA, Singapore organizations must make reasonable security arrangements to protect personal data. PDPC guidance covers risk-based authentication, logging, audits and role-based access. It says authentication strength should reflect the potential harm to individuals, and it names multi-factor authentication as a more secure method (PDPC guide). For SSO this means the strength of your login should scale with what sits behind it. A portal showing visitor names deserves more than a password alone.
One local point deserves a mention. The Ministry of Digital Development and Information says that using NRIC numbers to prove identity is unsafe, because they are easy to obtain and invite impersonation. The Government is working with regulated sectors, including finance, healthcare and telecommunications, on sector-specific authentication guidance, and organizations still using NRIC numbers to authenticate should move away as soon as possible (MDDI). If any system you plan to place behind SSO uses NRIC-based verification, fix that first.

Perspective: identity is a physical security problem too
We work with system integrators, facility owners and security agencies across Singapore, Malaysia and the Philippines, and the pattern we see is consistent. Teams invest in identity for their IT systems and then run the security operations room on shared logins, a shared tablet at the guard post and a visitor book at the lobby. The attacker's cheapest path is often the weakest login, wherever it lives.
Our view is that SSO belongs in a wider rule: every person, whether employee, guard, contractor or visitor, should be a known identity with the least access needed, and every action should leave a record. That is why the platforms we build around virtual guard tours, visitor management and unified operations dashboards are designed around exception-based monitoring: people review what matters instead of staring at everything. The same principle makes SSO monitoring workable. You do not read every log line, you act on the anomaly.
When you evaluate any security platform, ours included, ask five questions: Which identity standards does it support? Can it enforce MFA through your IdP? Does it map roles to least privilege? Does it export audit logs? How are sessions ended at offboarding? A vendor that answers these plainly is one you can put behind your login with confidence.
— Eumir
Bringing it together in the security operations room
A modern security operations center is a high-value application on your SSO. Video analytics, patrol records, visitor data and alarms all sit behind it, which means a compromised operator account can disable cameras or view sensitive footage. Treat operator roles as privileged: separate administrator and operator accounts, require stronger authentication for configuration changes, and review who holds which role on a fixed schedule.
If you are designing or upgrading such a room, our guides on a security monitoring workflow for facility teams and a PSIM-driven SOC pilot show how to structure roles and escalation. For a broader review of where identity fits among your other safeguards, use the security risk assessment checklist for facility owners.
Where BeyondSensor fits
SSO protects the digital door. Our work covers what happens at the physical one, and how the two are tied together in a single operating picture. BeyondSecure brings sensing and security operations into one unified view, while BeyondWatch handles video analytics and BeyondPatrol automates guard tours. If you are an integrator planning a multi-vendor deployment, our Solution Integration service helps you validate how the pieces connect, including identity requirements, before they reach the site.
To talk through your site, your identity setup and the security operations you need, start at BeyondSensor.
A practical rollout sequence
If you are starting SSO now, or tightening an existing deployment, this order keeps risk low.
- Inventory applications and owners. You cannot protect what you have not listed.
- Classify by data sensitivity. Personal data, video and access records go first on the stricter tier.
- Enforce phishing-resistant MFA at the IdP, starting with administrators and security consoles.
- Lock down the help desk. Require identity verification steps for resets that cannot be defeated by a convincing phone call.
- Protect signing keys with hardware-backed storage and a rotation plan.
- Map roles to least privilege and schedule access reviews.
- Turn on logging and alerting for failed logins, new devices and federation changes.
- Test offboarding. Disable a test account and confirm sessions end across every application.
- Reassess annually, and after any change to your IdP.
Avoiding common mistakes matters as much as the steps. Our note on security solution pitfalls to avoid in 2026 covers procurement errors that also apply when you buy an identity layer.
FAQ
Is single sign-on secure?
It is secure when the identity provider is protected with strong, preferably phishing-resistant, MFA, guarded signing keys and monitoring. It is risky when it is not, because stolen credentials can open many applications at once. SSO reduces password sprawl but raises the stakes on one login.
What is the biggest risk of SSO?
The biggest risk is a single point of failure. If an attacker captures a user's credentials or an assertion signing key, they may gain wide and persistent access across integrated applications (IDManagement). MFA, key protection and least privilege limit the damage.
Does SSO replace multi-factor authentication?
No. SSO is about signing in once, and MFA is about proving who you are when you do. They work together, and guidance from IBM and CSA treats MFA as a necessary part of any SSO deployment (IBM).
What should I check before enabling SSO for a new application?
Inventory the application, assess its risk, confirm it supports a standard such as SAML or OIDC, enforce MFA, map roles to least privilege and make sure it logs events to your monitoring. The table above turns these into a quick pre-connection test.
Does Singapore require SSO?
No rule we found requires SSO itself. The PDPA requires reasonable security arrangements for personal data, and PDPC guidance points to risk-based authentication, MFA, role-based access and logging (PDPC). SSO can be one way to meet those expectations.
Sources
- What is Single Sign-On (SSO) and How Does it Work? (Auth0)
- Choosing the Right Authentication Methods (CSA advisory AD-2025-015)
- Ongoing Campaign by SCATTERED SPIDER (CSA alert AL-2025-066)
- Enterprise Single Sign-On Playbook (IDManagement)
- Recommendation ITU-T X.1283 (09/2024)
- What Is Single Sign-On (SSO)? (IBM)
- Identity and Access Management Recommended Best Practices for Administrators (CISA)
- SEED Features and Roadmap (GovTech Singapore)
- Guide to Securing Personal Data in Electronic Medium (PDPC)
- Stopping the Use of NRIC Numbers as Passwords in the Private Sector (MDDI)
Recommended
Read More Articles
Line of Sight Survey: Methods, Tools and Site Checks
What a line of sight survey is, how surveyors and GIS analysts run one, and how to record results for CCTV, wireless and sensor deployments in Singapore.
Visitor Pre-Registration: A Practical Guide for Singapore Sites
How visitor pre-registration works at Singapore offices and industrial sites: what to collect, PDPA limits on NRIC and retention, QR check-in, and exception handling.
Fiber Optic Perimeter Security: How It Works and When to Use It
How fiber optic perimeter security detects and locates intruders, where it beats microwave sensors, and how to pilot it on a Singapore site.
Heatmap Analytics for Physical Security and Facilities
How heatmap analytics and footfall heatmaps work in buildings, how to read them, what limits their accuracy, and what Singapore's PDPA means for deployment.
Let's Build YourSecurity Ecosystem.
Whether you're a System Integrator, Solution Provider, or an End-User looking for trusted advisory, our team is ready to help you navigate the BeyondSensor landscape.
Direct Advisory
Connect with our regional experts for tailored solutioning.