See how zero trust, ISA/IEC 62443, mutual TLS, and API controls secure technology interoperability, from data schemas to practical IT/OT deployments.
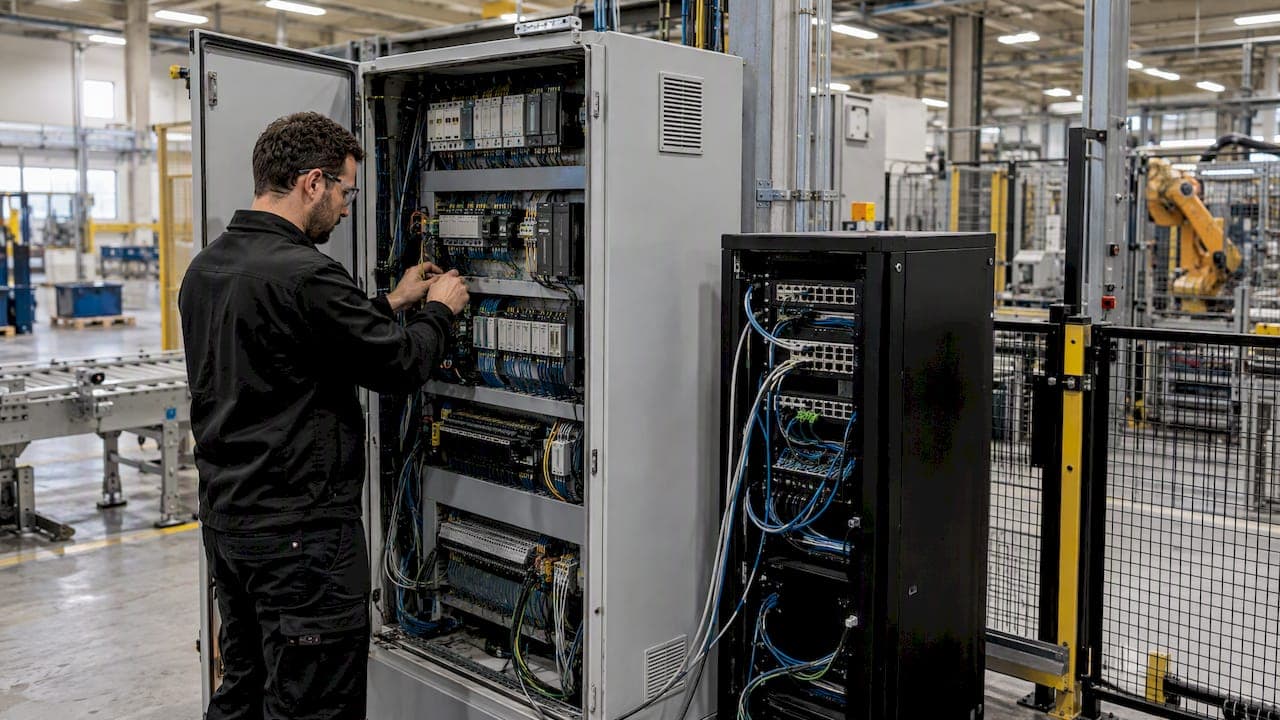
Secure Technology Interoperability: Bridge IT and OT with Zero Trust

A standards-led, zero-trust approach, applied across syntactic, structural, and semantic interoperability levels, is the practical way to make systems exchange data securely. NIST's zero trust architecture treats every connection as untrusted until verified, while ISA/IEC 62443 covers the operational technology side ISO/IEC 27001 was never built for. The sections below map these frameworks to concrete controls: mutual TLS, identity-based authorization, and API-level protections that hold up under real deployment conditions.
TL;DR:
- Treat interoperability at three levels: validate payload schemas and encryption, enforce versioned data contracts, and test shared vocabularies to catch meaning errors.
- Pair ISA/IEC 62443 for industrial availability and safety with ISO/IEC 27001/27002 governance; NIST zero trust continuously verifies service identities and secures API calls.
- Require mutual TLS, authorization based on identity, input validation, encryption in transit, and rate limiting on every API call, including internal traffic.
- For IT and OT links, use zone segmentation, protocol gateways, staged pilots, and tested rollback plans; adapt patching and monitoring to uptime and timing limits.
- Pilot each integration with real data, measure availability before expansion, and continuously monitor traffic with incident playbooks and recurring audits.
Table of Contents
- Levels of interoperability and what each demands from security teams
- Standards and frameworks that support secure interoperability
- Design-time and runtime controls for interoperable systems
- Bridging IT and OT: practical challenges and mitigations
- Implementation checklist and best practices for secure interoperability
- How sensor platforms implement secure interoperability
- Why standards-led, zero-trust interoperability matters now
- Secure interoperability support from BeyondSensor
- FAQ
- Sources
Levels of interoperability and what each demands from security teams
Interoperability is not a single capability. It breaks into three recognized levels, syntactic, structural, and semantic, and each one carries its own security burden, as the CBD's interoperability framework lays out.
Syntactic interoperability means two systems can exchange data in a format both understand, think JSON over REST, or a shared file structure. It is the baseline: without it, nothing talks to anything. Structural interoperability goes further, ensuring the data's organization and field definitions carry consistent meaning across the exchange. Semantic interoperability is the deepest level: systems not only exchange data but interpret it identically, so a sensor reading or a patient record means the same thing on both ends.
Each level raises different governance and security needs:
- Syntactic: requires schema validation and transport-layer encryption to prevent malformed or intercepted payloads.
- Structural: requires enforced data contracts (often via OpenAPI specifications) so a field cannot silently change meaning between versions.
- Semantic: requires shared vocabularies or ontologies, plus validation that a mapping error does not become a security or safety failure.
The artifacts that support each level matter for audits and incident response. An OpenAPI specification documents structural agreements. A shared vocabulary or taxonomy underpins semantic alignment. When a breach or malfunction occurs, these artifacts are often the fastest way to trace where an interpretation, rather than a connection, went wrong.
Standards and frameworks that support secure interoperability
No single standard covers interoperability security end to end, which is why practitioners combine frameworks built for different layers of the stack.
ISA/IEC 62443 is the horizontal standard for securing industrial automation and control systems, and it fills a gap that general IT security frameworks leave open: operational availability and safety. An ISA whitepaper on combining the two standards explains how ISO/IEC 27001 and 27002 controls map onto 62443's technical requirements, giving teams an integrated path rather than two competing rulebooks.
On the zero-trust side, NIST SP 800-207 shifts the security perimeter away from the network edge and onto individual service identities, using continuous verification instead of one-time authentication. NIST's API protection guidance builds on this by naming five runtime controls every cloud-native API should enforce: identification of non-person entities, mutual authentication (commonly mTLS), identity-based authorization, granular input validation, and encryption in transit.
For distributed ledger scenarios, ITU-T X.1415 specifies security requirements for gateways that connect heterogeneous blockchain systems, covering authentication, confidentiality, integrity, and auditing.
Together, these frameworks form a layered defense:
- ISA/IEC 62443 secures the operational and industrial layer.
- ISO/IEC 27001/27002 governs the organizational information security management system.
- NIST zero trust and API guidance secures the service-to-service and API layer.
- ITU-T X.1415 addresses gateway security for distributed ledger interoperability.
Design-time and runtime controls for interoperable systems
Securing interoperable exchanges is a life-cycle responsibility, not a single checkpoint. It starts before code is written and continues through every call a system makes in production.
- Design-time: adopt contract-first API design so the interface specification, not the implementation, is the source of truth, then validate every schema against it.
- Threat modeling: map data flows across trust boundaries during design, not after deployment, to catch exposure points early.
- Secure SDLC: bake security review into every build pipeline so interoperability interfaces are tested the same way core application code is.
- Runtime authentication: enforce mutual TLS and identity-based authorization on every call, internal or external, consistent with NIST's zero trust model.
- Runtime protections: apply encryption in transit, granular input validation, and rate limiting, the controls NIST's API protection guidance specifies for cloud-native systems.
- Observability: log and monitor API traffic continuously so anomalies surface before they become incidents.
- Testing: run fuzzing, replay testing, and semantic mapping validation to confirm that interfaces reject malformed or malicious input and that data retains its meaning across systems.
A zero-trust posture treats an internal service call with the same suspicion as an external one. That single shift, verifying identity and authorization on every hop rather than assuming internal traffic is safe, closes one of the most common gaps in interoperable architectures.
Pro Tip: Run semantic mapping validation as a recurring test, not a one-time check: vocabulary drift between systems is a slow leak, not a single failure.
Bridging IT and OT: practical challenges and mitigations
Connecting information technology with operational technology surfaces frictions that pure IT environments rarely encounter. Protocol mismatch is common: industrial systems often speak Modbus or OPC UA while IT systems expect REST or MQTT. Patching windows collide with uptime requirements, since a control system cannot always be taken offline on an IT team's schedule. Latency and determinism matter in OT in ways they rarely do in IT: a control loop that depends on predictable timing can fail unsafely if a security agent introduces delay.
This is precisely why ISA/IEC 62443 exists alongside ISO/IEC 27001 rather than in place of it. The ISA whitepaper on applying both standards together notes that standard IT patches or monitoring agents can break deterministic OT behavior when applied without adaptation.
Mitigations that preserve both security and safety:
- Zone-and-conduit segmentation: isolate OT zones and control what crosses each conduit, per 62443's core model.
- Protocol gateways: translate between IT and OT protocols at a controlled boundary instead of forcing OT devices onto IT standards.
- Staged pilots: introduce new interoperability links in a limited scope before full rollout, with defined success criteria.
- Rollback plans: maintain a tested path to revert any integration that threatens availability or safety.
Implementation checklist and best practices for secure interoperability
A practical rollout moves through three phases, each with its own priorities.
- Design phase: build a complete inventory of systems and data flows, maintain a specification registry (OpenAPI or gRPC definitions), assign named owners to each interface, and complete a threat model before any connection goes live.
- Pilot phase: deploy mutual authentication gateways, run semantic mapping tests against real data samples, and measure availability impact before scaling beyond the pilot.
- Scale phase: centralize policy enforcement across all interfaces, automate patching in a way that respects OT service windows, and establish continuous monitoring with defined incident playbooks.
- Governance: vet every new integration partner, log all cross-system traffic, and schedule recurring audits against the standards already in place.
A standards-based framing matters here. Analysis comparing interoperability and security tradeoffs finds that the common assumption, that interoperability inherently weakens security, is often overstated: a vetted interoperation conducted under zero-trust principles tends to reveal hidden vulnerabilities rather than create new ones. Treating the checklist above as a discovery tool, not just a compliance exercise, is where that benefit shows up.
How sensor platforms implement secure interoperability
Sensor-based security deployments make these principles concrete. Hardware feeds, video analytics, and access control systems each speak different protocols, and achieving structural and semantic alignment between them, so a motion event and an access log describe the same incident the same way, requires the same contract-first, zero-trust discipline outlined above.

Our Solution Integration service applies this directly: mapping multi-vendor sensor and software interfaces into a coherent, secured architecture rather than a patchwork of point connections. Ecosystem Matchmaking extends that work to partner and vendor selection, so new integrations are vetted before they touch a live environment.
Within our platform lines, we have products that combine sensor hardware with analytics software, requiring the structural and semantic mappings this article describes. Other products depend on runtime identity and authorization controls to keep automated monitoring and visitor data exchanges secure across systems.
Why standards-led, zero-trust interoperability matters now
Treating interoperability and security as competing goals is a dated frame. The evidence points the other way: a standards-led interoperation under zero-trust principles tends to surface the vulnerabilities that a closed, siloed system would have hidden indefinitely. That is a resilience gain, not a tradeoff.
Regulatory pressure and the sheer growth of connected IT and OT environments make this an active decision, not a future one. Every new integration is a chance to either harden the architecture or quietly expand its attack surface. The teams that treat interoperability governance as a shared responsibility across IT, OT, and security, rather than a project handed to a single group, are the ones who catch mapping errors and protocol mismatches before they become incidents. Start with one pilot, apply the full control set to it, and expand from evidence rather than assumption.
— Eumir
Secure interoperability support from BeyondSensor
Mapping protocols, vetting vendors, and building the mutual-authentication layer a secure integration needs takes real engineering time, and we built our service lines to carry that load directly rather than leave it to internal teams stretched across other priorities.
Our Solution Integration service handles the technical work of connecting sensor hardware, analytics platforms, and existing security systems under a single, secured architecture. When the challenge is finding the right vendor or partner rather than the integration itself, Ecosystem Matchmaking narrows that search to vetted options suited to the deployment.
- Start with a technical discovery conversation to scope the integration.
- Pilot a secured interface before committing to full-scale deployment.
- Bring existing vendor relationships into a coordinated, zero-trust architecture.
Reach out through our contact page to scope a pilot for your environment.
FAQ
What is the role of interoperability in health information technology?
In health information technology, interoperability allows patient records, lab results, and device data to move between systems while retaining consistent meaning, which is why semantic interoperability matters most in this setting. Secure implementations pair this data exchange with encryption, identity-based access controls, and audit logging to meet both clinical and privacy requirements.
What is another word for "interoperable"?
Common alternatives include "compatible," "integrated," and "interconnected," though each carries a slightly different technical emphasis. "Interoperable" specifically implies that systems can exchange and correctly interpret data, which is a higher bar than simple compatibility.
What is interoperability in IoT?
In IoT, interoperability means devices from different manufacturers can exchange data and act on it consistently, often across varied protocols like MQTT, CoAP, or Zigbee. Achieving this securely requires the same layered approach described above: syntactic compatibility at the protocol level, plus identity and encryption controls at the connection level.
What does "interoperable" mean?
"Interoperable" describes the ability of different systems, devices, or software to exchange data and use it correctly without special effort from the end user. It spans three recognized levels, syntactic, structural, and semantic, as outlined in the CBD's interoperability framework, each requiring progressively deeper agreement on data format and meaning.
Sources
- ISA — ISA/IEC 62443 series of standards
- NIST SP 800-207 — Zero trust architecture
- NIST — Guidelines for API protection (2026 update)
- ITU-T X.1415 — Security requirements for DLT gateway interoperability (2026)
- CBD — Interoperability levels (syntactic, structural, semantic)
Recommended
Read More Articles
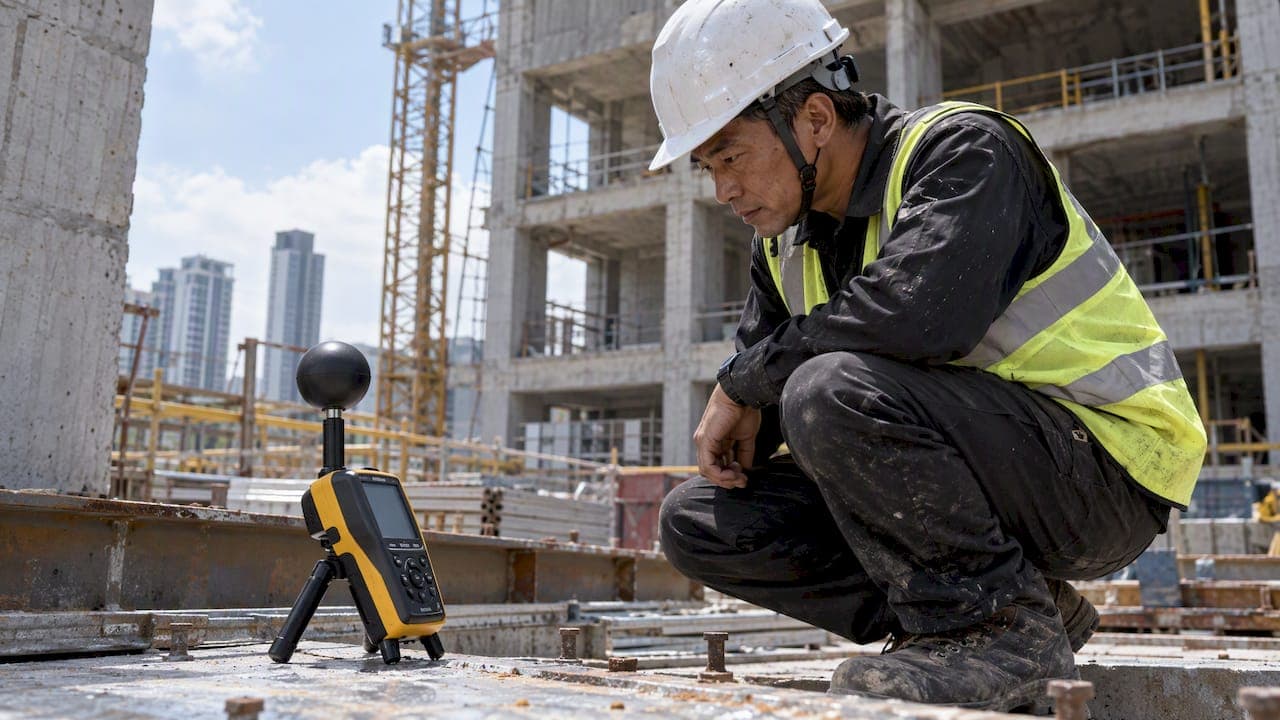
Heat Stress Monitoring for Singapore Safety Managers: The 32°C Rule
Singapore safety managers can monitor heat stress with hourly WBGT readings, apply the 32°C rest rule, and vet wearable alerts before relying on them.
Installers, Find the Signal Peak in Photoelectric Beam Alignment
Align photoelectric beams with gunsights, lasers, and signal readouts. Read AQ, RX, and IR, then lock the optics and verify with a cover test.
Smart City Noise Monitoring for Planners: Edge Privacy at the Source
Learn how planners combine reference stations, wireless sensors, and edge analytics to map noise, identify sources, protect privacy, and plan deployments.
Regional Validation Testing: 5 Risk Areas for Singapore Software Teams
Plan regional validation testing with NASA and Tricentis, Singapore PDPC and IMDA checks, and BrowserStack or Tailscale to prepare pilots for audits.
Let's Build YourSecurity Ecosystem.
Whether you're a System Integrator, Solution Provider, or an End-User looking for trusted advisory, our team is ready to help you navigate the BeyondSensor landscape.
Direct Advisory
Connect with our regional experts for tailored solutioning.