How to control contractor access in Singapore: credentialing checks, a third-party access policy, WSHA duties, and a step-by-step process from approval to offboarding.
Contractor Access Control: A Practical Guide for Singapore Sites

Contractor access control is the set of rules, records and tools that decide which outside workers may enter your premises or systems, where they may go, for how long, and how that permission ends. In Singapore it rests on three things: verified credentials before arrival, time-limited and role-based permissions during the work, and automatic revocation when the job closes. This guide walks security managers, facility owners and integrators through each one.
TL;DR
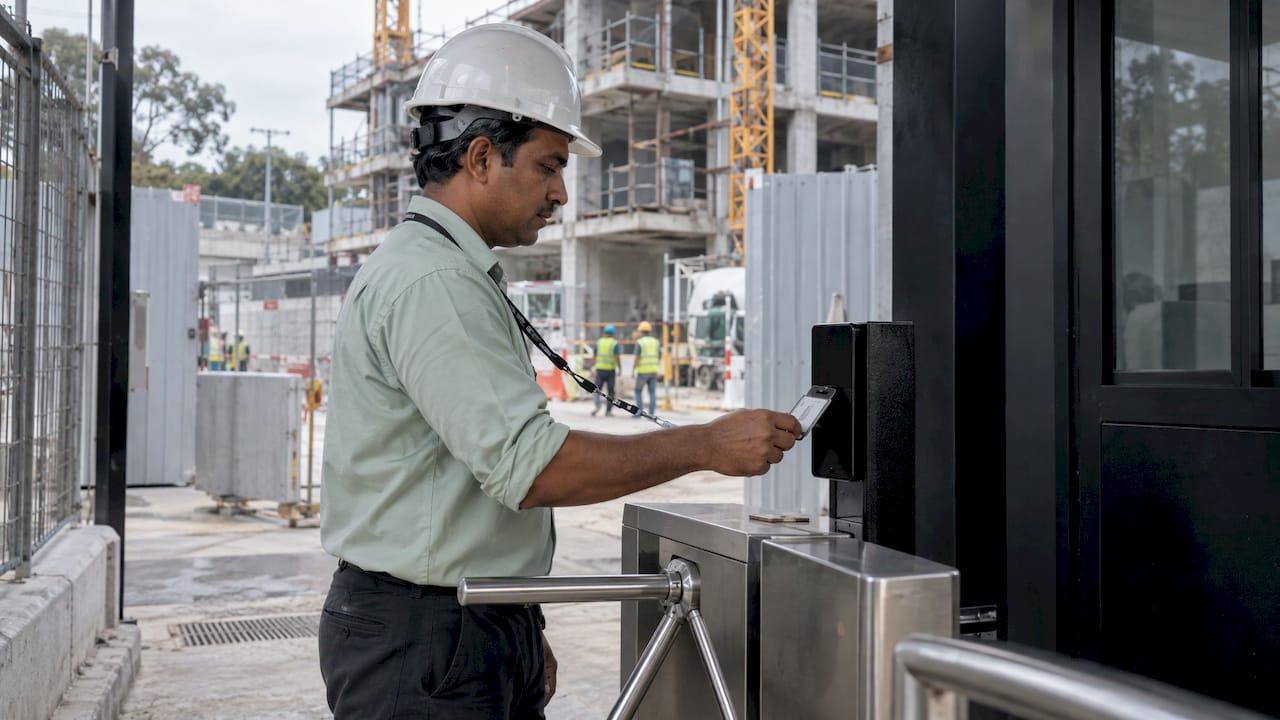
- Treat contractor access as a lifecycle: pre-approval, credential check, site entry, monitoring, offboarding. Gaps usually appear at the last step, when passes are never closed.
- Under the Workplace Safety and Health Act, a principal must take reasonably practicable steps to confirm a contractor's expertise, licences and risk assessment. A contract clause alone is not a defence.
- Grant least-privilege, time-boxed access tied to a named work scope, with escort rules for sensitive areas.
- Log every entry and review access on a fixed schedule so expired or unused credentials are removed.
- Digital pre-registration, role-based permissions and exception-based monitoring reduce manual checking at the gate.
Table of Contents
- What contractor access control covers
- Why Singapore organisations put it in place
- What contractor credentialing should check
- What a third-party access policy should say
- The contractor access process, step by step
- Controls that keep access tight
- Where technology helps across multiple sites
- How BeyondSensor supports contractor access programmes
- Common mistakes to avoid
- FAQ
- Sources
What contractor access control covers
A contractor and temporary worker access policy sets the rules for granting, monitoring and revoking physical and digital access for non-permanent staff. VantageSpace's Singapore glossary describes the typical contents: identity verification, badge issuance and expiry, permitted floors and rooms, IT and network privileges, escort requirements for sensitive areas, rules on photographing or recording, confidentiality agreements, background checks where required, and revocation when work ends. It also calls for logging, periodic reviews and named roles for approvals and audits.
That definition matters because contractors are different from employees and from visitors. Employees are onboarded through HR. Visitors come for a meeting and leave. Contractors sit in between: they stay for days or months, work in plant rooms, ceilings, server rooms and loading bays, and often bring their own subcontractors. Their access is more likely to be forgotten, shared or left open after the job.
People search for this topic under several names: contractor credentialing, third-party access policy, contractor access policy. They describe the same programme from different angles. Credentialing is the proof of who the person is and what they are qualified to do. The policy is the rule set. Access control is the enforcement at doors, turnstiles, networks and dashboards.

Why Singapore organisations put it in place
Three pressures push in the same direction.
Safety duty. The Workplace Safety and Health Act requires principals to take reasonably practicable measures to ensure contractor safety, including contractor expertise, adequate safety measures and risk assessment. Section 14A applies to contractors engaged on or after 1 September 2011. The consolidated text, in force from 1 December 2025, adds that the principal must, so far as reasonably practicable, ascertain that contractors and their employees have sufficient experience and training, the necessary licences, permits or certificates, and that the contractor has conducted a risk assessment. The same text states that a principal cannot rely solely on a contract term requiring the contractor to comply with WSHA duties as a defence to a Section 14A offence.
In practice, this means you need records. A signed agreement is not enough; you need evidence that someone checked.
Data protection. Contractors who handle personal data, or who can see screens, files and CCTV footage, create PDPA exposure. The PDPC's guidance on preventing accidental disclosure notes that an organisation may be held liable for the acts or omissions of its data intermediaries that breach a Data Protection Provision, and should make sure contracts impose sufficient obligations on them. If a contractor can open a server room or a records store, that applies to you.
Operational burden. Manual passes, spreadsheets and emailed lists do not scale across multiple sites. A clear policy, least-privilege access and automated offboarding lower both the workload and the legal risk tied to long-forgotten credentials, as the VantageSpace glossary also points out.
What contractor credentialing should check
Credentialing answers two questions: is this firm competent, and is this individual who they say they are and allowed to do this work?
Company-level checks
For construction and building works, the BCA's registration schemes are a useful benchmark for what a credible contractor file contains. The Contractors Registration System covers about 50 workhead types grouped under five registration groups, with separate requirements for financial standing, track record and personnel. Applicants prepare recent ACRA BizFiles (no more than one month old), management or audited accounts, NRIC, S Pass or Employment Pass details for key personnel, CPF Form 90 for local and PR employees, SGWorkpass screenshots showing employer and work pass expiry for foreign personnel, education certificates and relevant licences.
Under the Builders Licensing Scheme, a builder must appoint an Approved Person who directs the management of building works and a Technical Controller who oversees execution and performance. Knowing who holds those roles tells you who to call when something goes wrong.
You do not need to replicate BCA's process for a fit-out or maintenance vendor. But the logic transfers: confirm the entity, confirm the people, confirm the licences, and note expiry dates.
Individual-level checks
NTU's Contractor Safety Handbook is a good example of site-level requirements in Singapore. It requires a valid Construction Safety Orientation Course (CSOC) for all workers on any A&A works, WICA insurance and suitable third-party liability insurance for everyone on site, and visible identification such as company-named clothing or name tags with the company logo. It also treats contractors holding bizSAFE Level 3 or equivalent as having the competency required under the WSH (Risk Management) Regulations.
A workable credential checklist for most Singapore sites:
- Government ID and, for foreign workers, a current work pass with its expiry date.
- Company registration and a named supervisor responsible for the crew.
- Trade licences or certificates relevant to the task, such as safety orientation or equipment competence.
- Insurance evidence for the workers and for third-party liability.
- Signed acknowledgment of site rules, including photography and confidentiality terms.
- Risk assessment or method statement for the specific job.
Store the expiry date of each item. A credential that was valid in March may lapse in June, and your system should know.
What a third-party access policy should say
Write the policy once and apply it to every contractor, vendor and temporary worker. A strong one answers who approves, what is granted, for how long, and how it ends.
A Singapore example of how this looks in a regulated setting is the GXS Bank policy for third-party vendors. It requires need-to-know, least-privilege access to information assets, formal provisioning and de-provisioning, no concurrent access to production and backup systems, and documentation of access changes and approvals. The bank vets and approves user roles, permissions, access reasons and purposes, access periods and change requests, while the vendor must make sure access recertification is completed and approved on time. You are probably not a bank, but the structure is a sound template.
Cover these clauses:
| Clause | What it should state |
|---|---|
| Scope | Who counts as a contractor or third party, including subcontractors and agency staff |
| Sponsor | The internal employee who requests and owns the access |
| Approver | The role that approves, separate from the requester for sensitive zones |
| Permissions | Zones, hours, systems and data, defined by work scope |
| Duration | Start and end date, with extension through a new approval |
| Escort | Which areas require an escort, and who provides it |
| Recording | Rules on photography, screen capture and device use |
| Data | Confidentiality and personal-data obligations, mirrored in the contract |
| Revocation | Triggers (job complete, resignation of worker, incident) and who executes |
| Review | Frequency of access reviews and who signs them off |
Keep the policy short enough that site supervisors read it. Put the detail in forms and system settings, not in a forty-page document.
The contractor access process, step by step

1. Request and pre-approval
The sponsor submits the request before the work starts: company, worker names, work scope, locations, dates and hours. Pre-registration moves data entry out of the gate queue. Our guide to visitor pre-registration for Singapore sites covers the same principle for guests, and it applies directly to contractor crews.
2. Risk assessment and credential review
Before approval, confirm the contractor has assessed the risks of the job. The Workplace Safety and Health Council's guide for management corporations advises that risk assessments be conducted, as far as possible, in consultation with stakeholders such as premises owners, contractors and managing agents, considering personnel, work activities and environmental conditions. Use our security risk assessment checklist for facility owners to cover the security side of the same conversation. For hot work, confined spaces or work at height, link access to a permit: see how a digital permit to work ties approval, location and time together.
3. Screening and credential issuance
Verify identity documents and run any required screening. Where your site keeps a watchlist of barred persons, check against it at registration rather than at the gate, as explained in our piece on visitor watchlist screening. Then issue a credential: a QR code, a card or a mobile pass, valid only for the approved dates, hours and zones.
4. Site entry
At the gate, the system confirms the credential matches the registered person and the current time window. Staff handle only exceptions: an unregistered worker, an expired work pass, a crew member not on the list. Everything else flows through.
5. Monitoring during the work
Log entries and exits by zone. Compare the log with the approved scope: a plumber badge opening a data hall door should raise an alert. Review footage and activity logs when an exception happens, and apply privacy masking where footage shows people outside the incident. Our CCTV privacy masking and PDPA guide explains the setup.
6. Offboarding
Revocation should happen automatically at the end date, and earlier when the sponsor closes the job. Do not depend on an emailed reminder. Industry commentary on contractor badge revocation favours structured, machine-readable requests with timestamped acknowledgments over manual email. Record the revocation time so you can show an auditor that the access ended when the work did.
Controls that keep access tight
Physical and digital access follow the same principles. The Singapore Government's ICT&SS control catalogue for access control says access should be denied by default and granted only at the minimum permissions needed. It also requires disabling or removing accounts after a defined period of inactivity, reviewing access at a set frequency and removing unnecessary rights, rotating long-lived static credentials or using time-restricted ones, and keeping an inventory of accounts and their access rights.
Translate that into site practice:
- Deny by default. A new contractor credential opens nothing until a zone is assigned.
- Use roles, not individual exceptions. Define roles such as electrician, cleaner or network engineer, each with fixed zones and hours. Our role-based access control guide shows how.
- Time-box everything. Short validity, renewed by approval, beats open-ended passes.
- Issue individual credentials. Shared passes make logs meaningless.
- Handle IT access separately but consistently. ArkShield's vendor checklist for Singapore SMEs advises listing every vendor with system or data access, using dedicated vendor accounts, avoiding permanent admin rights unless necessary, using time-limited sessions and disabling accounts when no longer needed. If you federate logins, read our single sign-on security checklist.
- Review on a schedule. Monthly for high-risk zones, quarterly elsewhere, with the sponsor confirming each active credential.
Where technology helps across multiple sites
Once you manage more than one site or more than a handful of contractor firms, paper and spreadsheets break. Look for these capabilities, whatever platform you choose:
- One identity record per contractor worker, reused across sites.
- Pre-registration and approval workflows with expiry dates for each credential.
- Zone and time rules enforced at doors, turnstiles and lifts.
- A single dashboard showing who is on site now, across locations.
- Alerts for expired credentials, out-of-scope zones and overstays.
- Exportable logs for audits and incident reviews.
- Support for integrating hardware from different vendors, so you do not rebuild every site.
The last point is often the deciding one for system integrators. Most estates already run a mix of controllers, cameras and visitor kiosks.
Our perspective
Contractor access fails quietly. The gate works, the badge prints, and six months later nobody can say which crews still hold valid passes. We think the fix is to make the exception the only thing a person has to look at.
That is how we design our platform: automated checks at registration and entry, role-based zones, and exception-based monitoring so security teams respond to what is out of pattern rather than watching every door. Our approach combines AI-driven tools with multi-vendor integration, because Southeast Asian sites rarely run a single brand of hardware, and with localised technical validation, because Singapore, Malaysia and the Philippines each have their own compliance context.
The principle is simple. Verify before arrival, grant the minimum, expire by default, and keep a record you would be comfortable showing a regulator. AI never blinks at 3 a.m. at a loading bay, and that is exactly when a contractor access policy gets tested.
Eumir
How BeyondSensor supports contractor access programmes
Our BeyondVisitor product line is built for automated visitor management, and the same pre-registration, approval and entry logic extends to contractor crews. For sites that need the pieces to work together, our Solution Integration service plans and connects access control, video analytics and visitor workflows across multi-vendor environments, with deployment validated for regional requirements.
If you are an integrator or a security team scoping a contractor access rollout, you can start from our main site and tell us the number of sites, the contractor volumes and the systems already in place.
Common mistakes to avoid
- Relying on the contract alone. As the WSHA text notes, a contractual compliance clause is not a defence by itself. Keep checks on file.
- Open-ended passes. Every credential needs an end date.
- Ignoring subcontractors. Require the main contractor to list every worker before arrival, and make them accountable for it.
- Treating IT and physical access separately. A contractor who is badged out of the building can still hold a live VPN account.
- No owner for offboarding. Name the role that executes revocation and the one that verifies it.
- Collecting more data than needed. Gather what the checks require, store it securely and delete it on schedule, in line with PDPA obligations.
FAQ
What is the difference between contractor access control and visitor management?
Visitor management handles short, one-off visits, usually with a host and a meeting. Contractor access control handles repeated or extended entry for work, so it adds credential checks, work-scope permissions, zone and time rules, and a formal end date. The two can share one platform and one registration flow.
Who should approve contractor access?
The internal sponsor requests it, and a separate approver confirms it, especially for sensitive areas such as server rooms or plant rooms. The GXS Bank vendor policy shows the pattern: the organisation vets and approves roles, permissions, purposes, access periods and change requests. Name the approver role in your policy so approval never depends on one person.
How often should contractor access be reviewed?
Set a fixed frequency and keep to it. The Singapore Government's control catalogue requires access reviews at a defined frequency and removal of unnecessary rights within a defined number of days. Many teams review high-risk zones monthly and others quarterly, and every credential is also closed automatically at its end date.
Does the WSHA apply to security and facility teams?
It applies to the principal that engages the contractor, which is often the facility owner or occupier. The principal must take reasonably practicable steps to ascertain expertise, licences, permits and a completed risk assessment. Confirm how this applies to your premises with your WSH officer or legal adviser.
Sources
- VantageSpace: Contractor and Temporary Worker Access Policy
- Workplace Safety and Health Act 2006, Section 14A (Singapore Statutes Online)
- Workplace Safety and Health Act 2006, consolidated text
- PDPC: Guide to Preventing Accidental Disclosure
- BCA: Contractors Registration System
- BCA: Builders Licensing Scheme
- NTU Contractor Safety Handbook
- GXS Bank: Policy for Third Party Vendors
- Workplace Safety and Health Council: Guide for Management Corporations
- Singapore Government ICT&SS: Access Control catalogue
- ArkShield: Vendor Cybersecurity Checklist
- TeamBridge: Contractor Badge Revocation
Recommended
Read More Articles
Visitor Management Policy: What to Include for Singapore Sites
Build a visitor management policy for a Singapore workplace: scope, check-in rules, PDPA and NRIC limits, retention, escorts, emergencies and review.
Dust Monitoring Sensors: How to Choose and Deploy Them in Singapore
How dust monitoring sensors work, what Singapore rules expect, and how to choose, calibrate and connect them for construction and industrial sites.
Abandoned Object Detection: How It Works and How to Deploy It
How abandoned object detection works, how it tells an unattended bag from a paused one, how it differs from loitering detection, and what to check in Singapore.
Bridge Monitoring Sensors: Types, Placement and Data Use
Which sensors monitor bridges, what each measures, how data reaches engineers, and how to specify a system for Singapore infrastructure and facility owners.
Let's Build YourSecurity Ecosystem.
Whether you're a System Integrator, Solution Provider, or an End-User looking for trusted advisory, our team is ready to help you navigate the BeyondSensor landscape.
Direct Advisory
Connect with our regional experts for tailored solutioning.