Avoid 90 Second Chaos: Visitor Watchlist Screening for Singapore Teams
Practical, compliance-first playbook for visitor watchlist screening: SOPs, vendor requirements, PDPA and IMDA guidance, and BeyondSensor integration tips...
Avoid 90 Second Chaos: Visitor Watchlist Screening for Singapore Teams

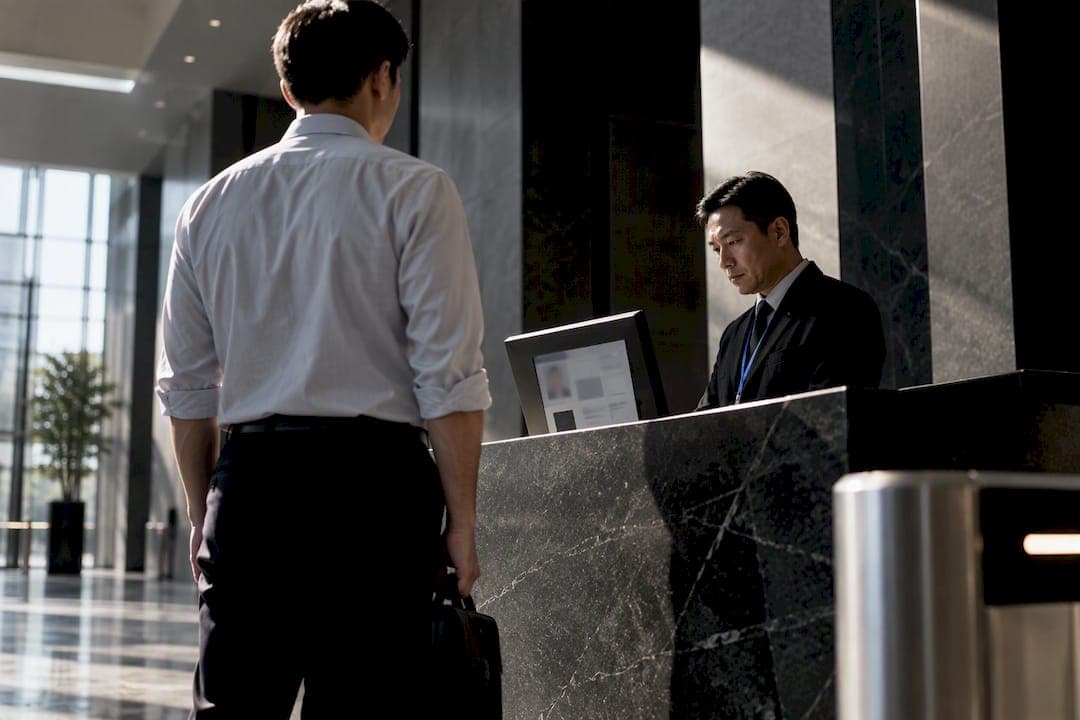
The most reliable approach to watchlist screening is integrating checks directly into your visitor management system, so every sign-in triggers an automated match against your active lists before a badge prints. Two constraints govern how you do this well: every check must be logged for audit purposes, and any biometric capture must follow PDPA-aware consent and retention practices. The sections below walk through the operational SOPs and legal guardrails that make this work in practice.
TL;DR:
- Proper watchlist screening should be integrated into visitor check-in systems, automatically matching sign-ins against active lists before badge issuance.
- The most relevant lists for daily operations are internal blacklists and whitelists, which require strict governance and accurate, current data management.
- A clear escalation process must be established for confirmed or high-confidence matches, including secondary verification and documented decision-making.
- Biometrics for access control require explicit consent, liveness detection, high thresholds, and limited data retention to comply with legal standards like Singapore's PDPA.
- Vendors should offer built-in watchlist checks, real-time alerting, secure biometric safeguards, and seamless integration with existing security infrastructure.
Table of Contents
- What Is Visitor Watchlist Screening and What Should You Expect From It
- Which Watchlists Facilities Commonly Check and Their Limits
- How Screening Fits Into the Visitor Check-In Workflow
- Privacy, Biometrics and the Legal Controls You Need
- Building an SOP for Handling a Watchlist Match
- What to Require From a Watchlist Screening Vendor
- A Quick Checklist to Assess Your Current Readiness
- Lessons From Real Watchlist Screening Deployments
- Why Most Facilities Get Watchlist Screening Wrong
- How BeyondSensor Supports Compliant Visitor Screening
- Sources
- FAQ
What Is Visitor Watchlist Screening and What Should You Expect From It
Watchlist screening is the automated comparison of a visitor's identity, typically a name, photo, or ID document, against one or more reference lists at the point of check-in. The goal is to catch a known risk before that person reaches a lobby, floor, or restricted zone, not after.

Facility and security managers deploy this capability for three practical reasons: to prevent entry by individuals barred for safety or legal reasons, to satisfy compliance obligations tied to regulated industries, and to protect physical or intellectual assets from repeat offenders or flagged individuals. None of these outcomes depend on catching every possible threat. They depend on catching the ones already known to your organization or to a relevant authority.
A match result is a flag, not a verdict. Most systems return one of a few outcomes:
- Clear: no match found, visitor proceeds through normal check-in.
- Potential match: a partial or lower-confidence match that requires human review before granting or denying access.
- Confirmed match: a high-confidence match against a high-priority list, typically triggering an automatic hold.
- System error: incomplete data or a failed query, which should always route to manual verification rather than default approval.
Treating every flag as an automatic denial creates unnecessary friction and legal exposure. Treating every flag as background noise defeats the purpose of screening at all.
Which Watchlists Facilities Commonly Check and Their Limits
Not every list belongs in every screening workflow, and each category carries its own scope and blind spots.
- International sanctions lists cover individuals and entities restricted from financial or trade dealings by governments or multilateral bodies. They are useful for corporate compliance but rarely designed to flag walk-in physical security risks.
- Criminal records and registries vary widely in public availability. Many jurisdictions restrict access to certified background-check providers, so a facility cannot simply query a criminal database in real time without a proper data-sharing agreement.
- Denied-party and government restricted lists target specific regulatory concerns, such as export control or immigration enforcement, and typically apply to a narrow set of industries rather than general visitor traffic.
- Internal corporate blacklists and whitelists are the most operationally relevant for day-to-day facility security. These are lists your own organization maintains: former employees terminated for cause, individuals under a restraining order, or approved contractors and VIPs who should bypass extra screening steps.
Internal lists require the most governance because they are entirely your responsibility to keep accurate, current, and defensible if challenged.
How Screening Fits Into the Visitor Check-In Workflow
Screening works best when it happens in layers, starting before the visitor ever reaches your building.
- Pre-registration screening: when a host submits a visitor's name and details in advance, the system runs the watchlist check hours or days ahead of arrival, giving staff time to review any flag without holding up a line at the door.
- On-site kiosk or desk check: for walk-ins or as a final identity confirmation, the kiosk captures a document scan, photo, or one-time passcode verification and queries the same lists again in real time.
- Matching and threshold tuning: the system ranks list priority so permanent bans and government must-not-admit entries are checked first, with lower-priority lists like general sanctions data queued for manual review rather than triggering an automatic hold.
- Escalation on a match: a confirmed or high-confidence match pauses badge printing automatically, prompting a documented next step, whether that is a secondary ID check, a security escort, or an outright denial.
- Audit logging: every check, match or clear, is timestamped and stored according to your retention policy, both for internal review and for any external compliance reporting.
Pro Tip: Run pre-registration checks well in advance of a scheduled visit whenever possible, so a genuine match never becomes a same-day scramble.
This layered flow mirrors what facility owners in professional services environments already use for access control, extending the same identity-verification logic to the front door rather than just internal zones.
Privacy, Biometrics and the Legal Controls You Need
Biometric data carries a higher legal bar than a name or ID number, and treating it casually is the fastest way to turn a security tool into a compliance liability; understanding biometric enrollment and access workflows is critical, as explained in Biometric Access Explained for Home and Business Security — Safes and Security Solutions.
Under Singapore's PDPA, organizations capturing biometric data for access control typically need explicit consent or a documented legitimate-interest justification, along with clear notice to visitors about how their biometric samples will be collected, used, and stored, according to government commentary on face recognition technology. This is not a box-ticking exercise. It shapes how your signage reads, what your intake form says, and how long you keep a facial template after a visit ends.
Seek explicit consent when enrolling biometric samples for visitors, implement liveness detection, set high matching thresholds to reduce false positives, and restrict access to biometric records. PDPC's Guide to the Responsible Use of Biometric Technology
The PDPC's biometric guidance also recommends data minimization and defined retention limits, meaning you should not keep a visitor's biometric template indefinitely just because the storage is cheap.
IMDA's automated visitor management preapproval checklist treats blacklist and whitelist functionality as a mandatory capability for any vendor seeking approval in this solution category, which is a useful benchmark when evaluating a system regardless of where you deploy it.
Operationally, this translates to a few non-negotiable safeguards: restrict access to match records to a small, trained roster of security staff, post visible notice at check-in about what data is collected and why, and document your SOPs so a regulator or auditor can trace exactly how a match was handled. For hotels and similar guest scenarios, the Immigration EVA System order shows how far identity-verification requirements can go, specifying exact standards for facial-photo-to-passport matching at check-in.
Building an SOP for Handling a Watchlist Match
A match is only as useful as the process that follows it. Without a clear SOP, staff either freeze or wave the visitor through, and both outcomes defeat the point of screening.
- Initial hold: badge printing pauses automatically and the visitor is asked to wait in a designated area, never left standing at an open door.
- Secondary verification: front desk staff compare a government ID or passport photo against the system's flagged image, a check that should take under two minutes.
- Escalate to a security supervisor: any match that survives secondary verification goes to a named supervisor, not a general security mailbox, within a fixed response window.
- Apply the decision matrix: the supervisor chooses among escort with restricted access, outright denial, or contacting authorities, based on which list triggered the match and its documented risk level.
Pro Tip: Build your decision matrix before your first real match happens. Deciding escalation rules in the moment, under pressure, is how organizations end up with inconsistent or legally shaky outcomes.
False positives are the operational tax you pay for screening at all, and managing them well protects both security and visitor experience. Tuning matching thresholds too loosely floods your front desk with holds for people who share a name with a flagged individual. Set thresholds high enough to reduce that noise, run periodic test exercises with known clear profiles, and give staff a defined manual review window rather than an indefinite wait.
Maintenance is not optional either. Internal blacklists need a review and purge schedule so former employees or resolved disputes do not stay flagged years after the fact. Keep a change log for every list update, run periodic system health checks on your matching engine, and refresh staff training often enough that the SOP stays muscle memory rather than a forgotten binder.
What to Require From a Watchlist Screening Vendor
Procurement teams evaluating a visitor management system should treat certain features as baseline requirements, not upgrades.
- Watchlist hooks built into check-in, meaning the system queries lists automatically rather than as a bolt-on integration.
- Kiosk or desk-based photo capture and OTP verification to confirm identity at the point of entry, not just on paper.
- Logging and alerting that timestamps every check and routes confirmed matches to a named responder immediately.
- Feed integration with the identity sources relevant to your risk profile, whether that is a corporate HR directory, internal lists, or a sanctions feed.
- Biometric safeguards including on-device enrollment, liveness detection, multimodal authentication, and encryption for any stored template.
- API-first design so the platform can connect to access control, CCTV snapshots, and event logging systems as your security stack grows.
A vendor unwilling to detail how these pieces connect is asking you to take compliance and operational risk on faith.
A Quick Checklist to Assess Your Current Readiness
Use this as a working audit rather than a wish list.
- Immediate: confirm your policy aligns with PDPA consent requirements, post visitor-facing signage, verify your vendor's feature list includes blacklist and whitelist functionality, and run a daily test of match alerts.
- Within 30 days: pilot false-positive scenarios with staff, run SOP training sessions, and draft a data retention and purge policy for biometric and match records.
- Within 90 days: integrate watchlist alerts with access control and CCTV systems, complete a documented DPIA for any biometric module, and run a tabletop exercise simulating a confirmed match end to end.
Lessons From Real Watchlist Screening Deployments
The most common pitfalls in these rollouts are data format mismatches between list feeds, unclear escalation ownership, and thresholds tuned too aggressively out of the gate. A staged rollout, pilot, tune thresholds, train staff, then scale, catches these issues before they become front-desk incidents. Platforms like BeyondVisitor and BeyondWatch are built around exactly this kind of staged, alert-driven workflow.

Why Most Facilities Get Watchlist Screening Wrong
The conventional advice treats watchlist screening as a technology purchase: buy a system with blacklist and whitelist functions, plug it in, done. That misses the actual failure point, which is almost never the software. It is the absence of a clear, rehearsed decision process for what happens in the ninety seconds after a match fires.
Facilities that invest heavily in matching accuracy while leaving escalation loosely defined end up with two failure modes: staff who freeze and let a flagged visitor through, or staff who over-correct and deny access to someone with a coincidental name match. Both erode trust in the system, from security staff and visitors alike.
If there is one priority worth front-loading, it is writing and rehearsing the SOP before optimizing the matching engine. A well-tuned threshold on a system nobody knows how to respond to is worse than a conservative threshold paired with a team that knows exactly what to do next. Get the human process right first. The technology is the easier half of this problem.
— Eumir
How BeyondSensor Supports Compliant Visitor Screening
Building a watchlist screening workflow that satisfies both security needs and privacy obligations takes more coordination than most facility teams have time for on their own. BeyondSensor's BeyondVisitor platform brings pre-registration checks, kiosk-based verification, and blacklist and whitelist management into a single workflow, while BeyondWatch handles the alerting and escalation side once a match fires.
For teams that need help connecting these tools to existing access control, CCTV, or HR directory feeds, BeyondSensor's Solution Integration service handles the deployment and configuration work directly. If you are evaluating your current setup or planning a first rollout, get in touch to schedule an integration assessment.
Sources
- Guide to the Responsible Use of Biometric Technology — PDPC (May 2022)
- Automated visitor management — IMDA pre-approval vendor self-assessment
- Immigration (Section 57(1)(d) — Exemption) Order 2022 — Singapore Statutes Online
- Parliament Q&A and related PDPA commentary — MDDI (Singapore government newsroom)
FAQ
What are the different types of watchlists?
Facilities typically screen against international sanctions lists, criminal records and registries where legally accessible, government denied-party or restricted lists, and internal corporate blacklists and whitelists. Each serves a different purpose, and internal lists usually carry the most day-to-day operational weight since your organization controls their accuracy directly.
Do I need visitor consent to collect biometric data?
Yes. Under Singapore's PDPA, organizations generally need explicit consent or a documented legitimate-interest basis before capturing biometric data for access control, along with clear notice about how the data will be used and stored, per government guidance on face recognition.
How do I reduce false positives in watchlist screening?
Set matching thresholds high enough to limit coincidental name or image matches, and build in a secondary verification step using a government ID or passport photo before escalating further. The PDPC's biometric guidance specifically recommends high thresholds and liveness detection as part of this process.
What should happen when a visitor triggers a match?
The system should pause badge printing automatically while front desk staff perform a secondary identity check against the flagged record. If the match holds up, it escalates to a named security supervisor who applies a documented decision matrix covering escort, denial, or contacting authorities.
What features should a visitor management system include for screening?
At minimum, look for automated watchlist hooks at check-in, photo or OTP-based identity capture, real-time logging and alerting, and blacklist and whitelist functionality, which IMDA's preapproval checklist treats as a mandatory capability. Some platforms build these functions directly into the check-in workflow rather than as separate add-ons.
Recommended
Read More Articles
97% Takeover Success Demoed: Sensor Fusion Security for Practitioners
For security teams and system integrators: harden sensor fusion security with ETSI hardware controls, documented attack evidence, and a practical...
Stop False Dispatches: 5 SOP Steps for Singapore Alarm Triage
SOP first, verification led alarm triage workflow for Singapore facilities. Five SOP steps aligned to PDPC, SGPolice and ABS guidance.
Singapore Procurement: Live Pilot for Intrusion Detection Analytics
Procurement-first checklist for Singapore teams: require live pilots, add PDPA checks to RFPs, and judge intrusion detection analytics by pilot results...
Avoid Outages: IMDA/JST Camera Firmware Management for Administrators
Practical operations-first guidance for security administrators to run staged, auditable firmware updates across multi-site camera fleets, aligned to IMDA...
Let's Build YourSecurity Ecosystem.
Whether you're a System Integrator, Solution Provider, or an End-User looking for trusted advisory, our team is ready to help you navigate the BeyondSensor landscape.
Direct Advisory
Connect with our regional experts for tailored solutioning.